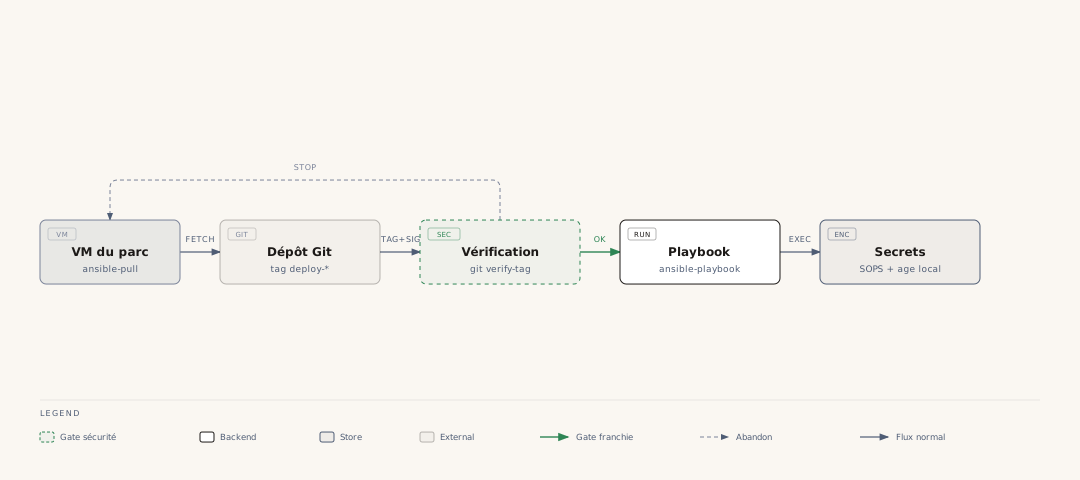
GitOps without Vault: reducing blast radius by verifying instead of storing
· 12 min read

Deploying a fleet of VMs with no central server pushing configuration, no secrets vault permanently exposed, and a simple question asked on every cycle: "was what I'm about to execute signed by someone authorized?" This post describes the pull-based GitOps architecture I built around that question, and why it mechanically shrinks the attack surface compared to a classic push model.