
2 posts tagged with "zero-trust"

View All Tags

SSH without static keys: 10-hour certificates backed by Entra ID

· 7 min read
BENE Maël
System Administrator

Replacing an admin team's static SSH keys with ephemeral certificates, issued on demand through OIDC authentication (Entra ID + MFA), valid for 10 hours. This post describes the architecture set up on a fleet of about ten VMs, and above all the two or three surprises you won't find in the docs until you've actually put it in production.
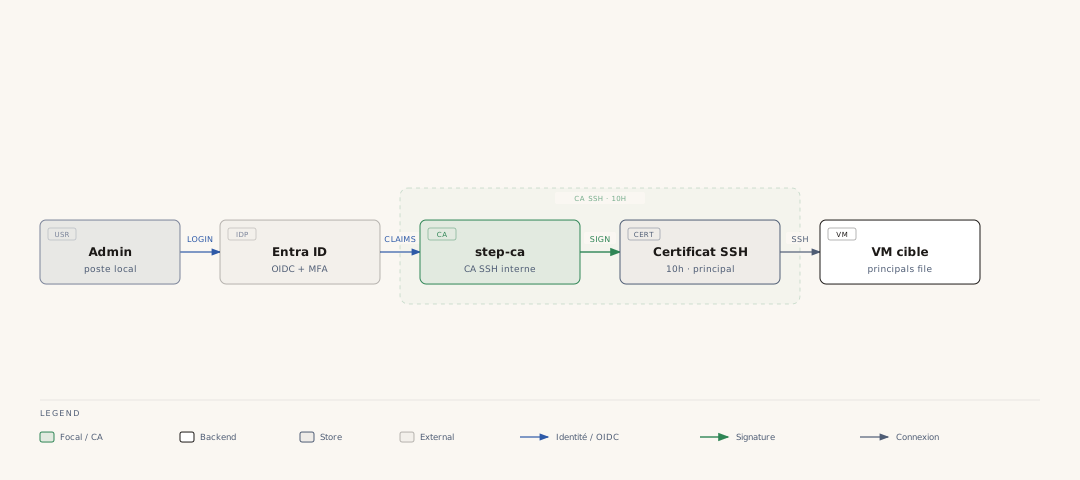
Flow diagram: an admin authenticates via OIDC against Entra ID, step-ca signs an ephemeral SSH certificate from the token's claims, which is then presented to the target VM

GitOps without Vault: reducing blast radius by verifying instead of storing

· 12 min read
BENE Maël
System Administrator

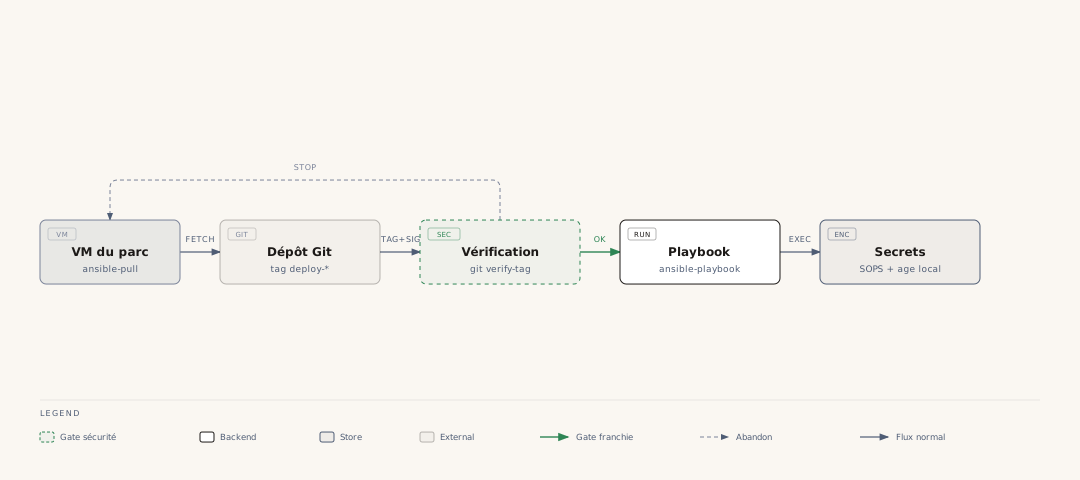
Deploying a fleet of VMs with no central server pushing configuration, no secrets vault permanently exposed, and a simple question asked on every cycle: "was what I'm about to execute signed by someone authorized?" This post describes the pull-based GitOps architecture I built around that question, and why it mechanically shrinks the attack surface compared to a classic push model.

Diagram of the ansible-pull pipeline: a VM fetches the Git repository, verifies the tag signature before any execution, runs the playbook only if verification passes, otherwise aborts without executing anything